Vulnerability Scanners and How to Protect Your Company From and With Them
Vulnerability scanners are often used during security audits. The goal: to be one step ahead of the cybercriminals!
Vulnerability scanners are often used during security audits. The goal: to be one step ahead of the cybercriminals!
Vor zehn Jahren war es noch eher selten, dass Hacker Unternehmen und IT-Infrastrukturen angriffen und mit Malware infizierten.
A bug bounty program and a penetration test are both important measures to improve the security level of a system. However, there are important differentiators between the two that need to be understood before deciding which one to use.
Learn about the most common initial attack vectors and their protection recommendations.
Do you like listening to podcasts? Get to know the best five cyber security podcasts.
KAPE-Einführung, Teil 4: Was wurde wann von wem ausgeführt?
KAPE-Einführung, Teil 3: Browserhistorie auswerten und verstehen
KAPE-Einführung, Teil 2: Autoruns-Artefakte auswerten und verstehen
Für den Exchange Server sind zwei weitere Zero-Day-Schwachstellen erkannt worden.
KAPE-Einführung, Teil 1: Installation, Konfiguration und Ausführung
Noch vor wenigen Jahren war das Thema Security im Bereich der Operational Technology (OT) im Vergleich zur klassischen IT kaum relevant. Dies änderte sich schlagartig, als erste – damals staatlich durchgeführte – Angriffe bekannt wurden. Heute sind Angriffe auf die OT bereits an der Tagesordnung.[1]
Makros in Microsoft-Office-Dokumenten (z. B. Word, Excel usw.) werden häufig von Angreifern missbraucht, um Code zu verstecken, der Schadsoftware herunterlädt oder ausführt, was zur Kompromittierung von Systemen führen kann. Auf modernen Systemen werden daher als Schutzmassnahme Makros standardmässig nur nach Erlaubnis des Nutzers gestartet.
Eine Grundabsicherung von Azure Active Directory und Microsofts Cloud-Diensten ist kein Hexenwerk. Doch um an den richtigen Stellschrauben zu drehen, gilt es, sie zunächst zu finden. Dabei helfen die Bordmittel des Admin-Portals, kostenlose Tools, Tipps aus dem Netz und vor allem das Verständnis von Microsofts Sicherheitskonzepten.
Beim Azure Active Directory (AAD) sind mangelnde Härtung und Fehlkonfigurationen der Dreh- und Angelpunkt, wenn es um die Angreifbarkeit des AAD und darüber abgesicherter Dienste wie Microsoft 365 und die IaaS- und PaaS-Angebote in Azure geht. Wer die typischen Angriffe kennt, weiß, worauf er achten muss.
Der Identitätsdienst Azure Active Directory kontrolliert den Zugriff auf Microsofts Cloud-Dienste von Azure bis Microsoft 365. Er ist ein beliebtes Angriffsziel – und standardmässig nicht gut gesichert.
Penetration test and red teaming are cybersecurity terms. But what exactly is red teaming? And what is a penetration test all about? What are the differences between the two terms?
Schwache Passwörter können von Angreifern leicht erraten und missbraucht werden. Damit können sie Aktionen ausführen, die von denen eines legitimen Benutzers kaum mehr zu unterscheiden sind.
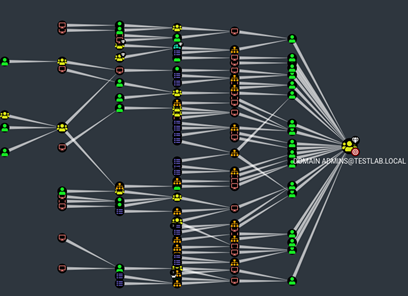
A modern Active Directory environment consists of many different components. There are clients, servers, databases, users, applications and much more. It is easy to lose track of everything (especially as a Red Team). The BloodHound tool can help here.
What are the most common security vulnerabilities in web applications? What does an attacker need to do to find and exploit them? And how can developers protect their web applications against them? Answers to these questions as well as practical hands-on examples are provided by PortSwigger’s Web Security Academy.
Ransomware has long been on everyone’s mind and part of daily news coverage. Oneconsult’s Digital Forensics and Incident Response specialists are regularly asked to present background information on such cyber attacks, discuss them and address the current threat situation. A central element is to show that all industries, company sizes and private individuals are affected by ransomware attacks and the associated risks.