Home | Services | Attack Simulation | Physical Access Assessment
Our Physical Access Assessment is a specific type of physical security assessment. We carry out realistic tests that use social engineering tactics such as tailgating and piggybacking, along with modern technology, to put your security measures through their paces. We gain physical entry to sensitive areas of your organization and test how well your access control systems and physical measures protect against unauthorized access. This uncovers vulnerabilities before malicious actors can exploit them.
Our Physical Access Assessment service simulates a complete attack cycle as it would happen in the real world, combining red teaming with social engineering. This lets us cover every dimension of security as part of a vulnerability assessment:


How effective your security measures are depends on how well technical, personnel, and structural safeguards work together. Our Physical Access Assessment service reviews these areas thoroughly and evaluates your organization’s overall level of security.
To cover all key aspects of security, you can combine the Physical Access Assessment with our technical Red Teaming service. This lets us assess whether we can move laterally within your internal network after planting malicious hardware in it.
A strong security strategy is only as good as its implementation in day-to-day work. Our Physical Access Assessment shows whether your employees are consistently complying with your security policies.
Our Physical Access Assessments are not off the shelf. We develop customized scenarios tailored specifically to your business risks and potential threats.
Our Physical Access Assessment service uses various social engineering tactics, including tailgating, piggybacking, priming, and elicitation. In addition, we use advanced technologies such as voice emulation and deepfakes and manipulate access control systems to test your defense strategies.
Our service is not limited to regular business hours. If you wish, we can conduct social engineering tests at night, on weekends, or on holidays to find weaknesses at the times when your organization is most exposed.
Our Physical Access Assessment service helps you identify your organization’s human, technical, and process-related vulnerabilities before attackers can exploit them. Our experts develop customized attack scenarios based on your specific risk profile. This allows you to make targeted improvements to your security measures and make sure your employees and processes hold up in practice.
Test your employees, technical safeguards, and processes in realistic scenarios. Our Physical Access Assessment service shows you whether your security measures work in practice and how to address any weaknesses.
A Physical Access Assessment is a realistic test in which Oneconsult tries to physically enter sensitive areas of a company. For this purpose, Oneconsult uses social engineering tactics such as tailgating and piggybacking. The test shows how well access control systems and physical measures protect against unauthorized access. The Physical Access Assessment is a specific form of physical security assessment.
A physical penetration test starts with in-depth OSINT research, on-site reconnaissance, and preparation. These phases can take several weeks, while the actual test often takes only a few minutes. In the Physical Access Assessment, Oneconsult simulates a complete attack cycle and combines red teaming with social engineering. The scenarios are based on the risks and threats of the company. On request, Oneconsult also tests at night, on weekends, or on holidays. For more information, see our blog post “Enhancing Cyber Resilience Through Attack Simulations According to DORA and TIBER”.
Oneconsult uses various social engineering tactics, including tailgating, piggybacking, priming, and elicitation. Oneconsult also uses voice emulation, deepfake technology, and the manipulation of access control systems. With these methods, Oneconsult puts the defense of a company to the test. Oneconsult develops the scenarios individually for the risks and threats of each company.
No, a social engineering test looks for processes that are not followed or that are missing. Oneconsult’s testers manipulate people, but they do not want to attack anyone emotionally or stir up fears. Oneconsult’s goal is for employees to feel better after a conversation than before. Personal attacks would cause employees to lose trust in their company. In the documentation, Oneconsult anonymizes all individuals and records no times.
Yes, you can combine the Physical Access Assessment with the technical red teaming from Oneconsult. The combination connects the testing of physical access points with the testing of technical security. Oneconsult checks whether the test team can move through the internal network after it has smuggled in malicious hardware.
Tailgating means following closely behind an authorized person without being noticed, for example through a door secured by badge access. The authorized person does not notice that an attacker slips through as well. For example, when a group returns from lunch, usually only the first person uses their badge. An attacker can simply walk along in this stream of people. In larger companies, anonymity and a lower sense of responsibility facilitate such attacks. For more information, see our blog post “Social Engineering: Introduction and Techniques”.
Companies protect themselves through employees who ask unknown people at the entrance and in protected areas whether they are authorized. This requires a culture in which employees are allowed to question unfamiliar people, including higher-ranking ones, without fear of consequences. The employees thoroughly check the reasons given for access. If in doubt, they call in the internal security service. Posters on walls or doors remind people to look over their shoulder when they enter protected areas. Technical measures such as mantraps and door opening alarms support these precautions. For more information, see our blog post “Social Engineering Prevention for Businesses”.
If a social engineering test is planned too tightly and is not realistic, the success of an attack is a matter of chance. Therefore, plan enough time for a professionally simulated and well-prepared attack. This attack can take place within a shortened but realistic test period. If the testers manage to break into a server room within one to two weeks, real attackers will also succeed. Real attackers have considerably more time available.
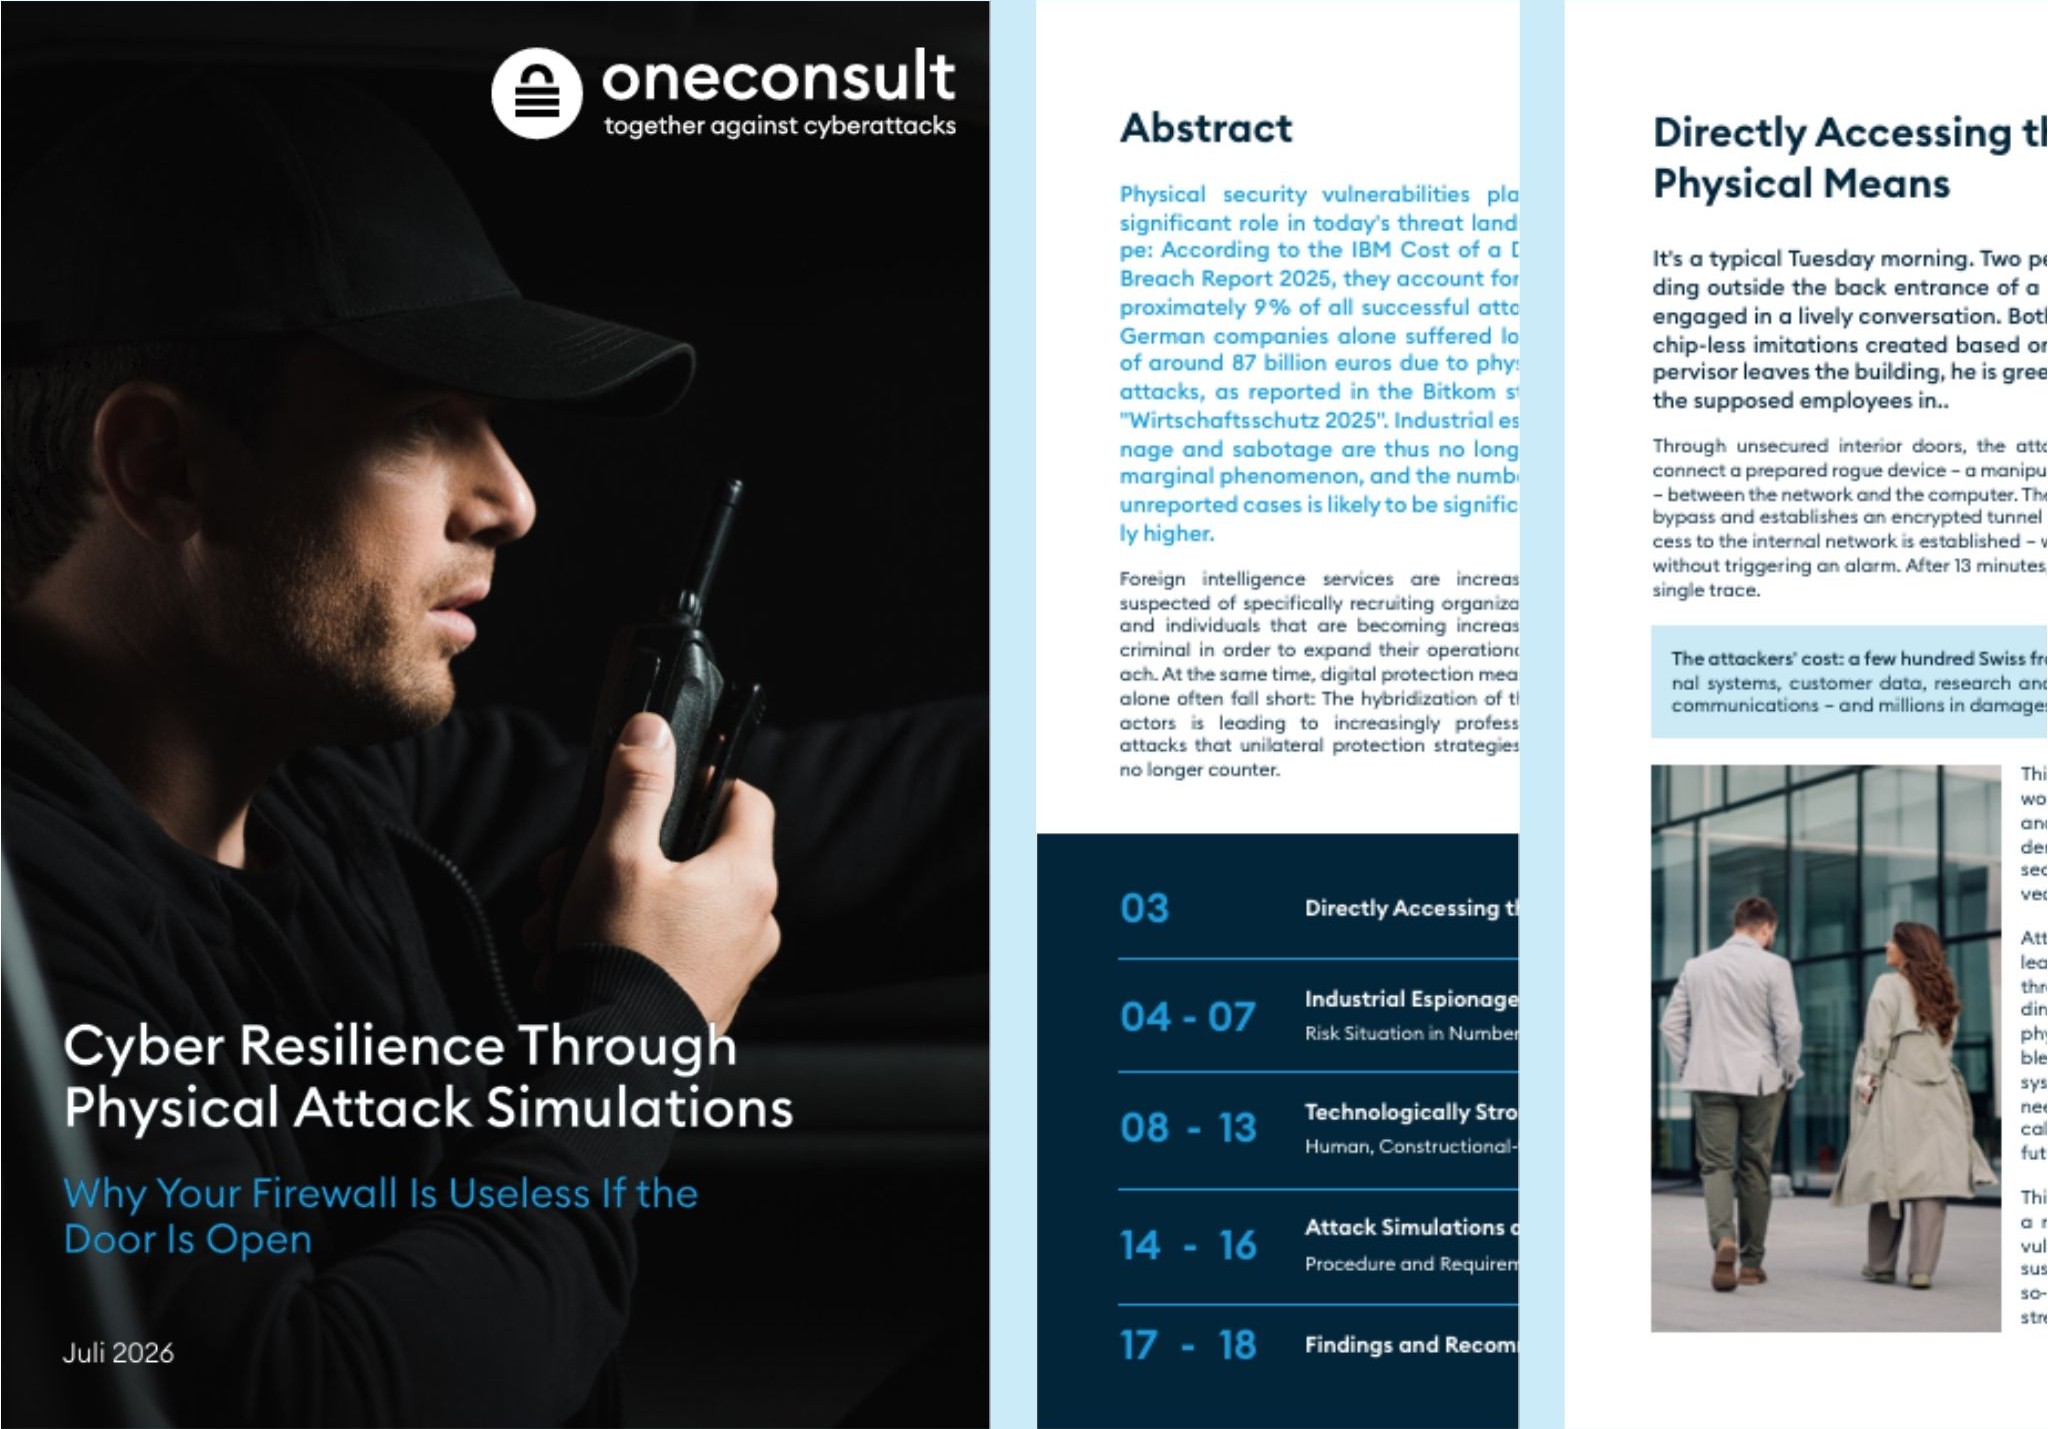
Your firewall offers little protection if the door is left open.
This white paper explains why physical attack simulations are an important component of modern cyber resilience.
Learn more about today’s threat landscape, the methodology behind Physical Access Assessments, and the most common vulnerabilities identified during real simulations.
Available Monday to Friday, 8:00 a.m. to 6:00 p.m. Exception: customers with an SLA should call the 24/7 IRR emergency number.
If you are a private individual, please contact your trusted IT service provider or your local police station.
You can find more information about our DFIR services here:
Don’t miss anything! Subscribe to our free newsletter.
