Home | Services | Attack Simulation | TIBER / DORA TLPT
This applies to the following organizations operating in the EU:
Our specialized TIBER team brings together experts from a wide range of disciplines: penetration testing, red teaming, digital forensics, incident response, building technology, and non-technical fields such as law enforcement, counterintelligence, and sabotage prevention. This interdisciplinary expertise allows us to assess your cyber and physical security risks as a whole.
For TIBER- and DORA-compliant Threat-Led Penetration Tests (TLPT), we rely on a well-coordinated team of experts with many years of experience. Our specialists are trained to compromise highly privileged accounts, access sensitive areas, and bypass existing security mechanisms, even in heavily hardened environments.
Oneconsult is an independent, owner-managed Swiss cybersecurity company with subsidiaries in Munich and Auckland. As an established and trusted partner, we are committed to integrity and security. Our employees undergo regular official background checks.
Targeted Threat Intelligence (TTI) is a threat analysis tailored specifically to your company. It helps you better understand potential attacks and develop targeted security strategies.
We conduct complex, multi-stage attack simulations based on the threat scenarios modeled in the TTI report. Red teaming targets the specific risks and vulnerabilities of your organization. This allows you to effectively test your cybersecurity measures and your ability to respond, and to strengthen your resilience against realistic attacks.
Not sure yet whether you will be required to undergo TIBER/DORA-compliant testing in the future, but want to be prepared? Even without a legal obligation, you can actively strengthen your cyber resilience. Our TIBER-based tests reveal vulnerabilities and potential attack paths that cybercriminals could use. With our recommended measures, you can then prepare your company for real-world threat scenarios in a focused and effective way.
Control Team (formerly White Team): The Control Team is the client’s coordination point throughout the TIBER test. It is responsible for overall risk management, monitors the test activities, and ensures that they stay within the agreed scope.
Blue Team: The defense team of the company under test is not aware of the test activities and is only informed afterward.
(Targeted) Threat Intelligence Provider: The external service provider conducts a threat analysis of the company in question and evaluates realistic attack scenarios.
Red Team: The external service provider acts independently of the Threat Intelligence Provider and conducts realistic attack simulations based on the TTI report to assess the company’s actual security level.
TIBER Cyber Team (TCT): As the national authority, the TCT supports the TIBER test on technical and procedural matters. It monitors compliance with the TIBER requirements and, in particular, helps the Control Team implement them correctly.
According to the TIBER framework, the Threat Intelligence Provider must act independently of the Red Team and be organizationally separate from it. However, this does not necessarily prevent one cybersecurity company from providing both services, as long as the requirements are met. Oneconsult has clearly separated business divisions for this purpose.

TIBER-EU and DORA TLPT are frameworks for threat-based tests that are intended to strengthen the cybersecurity and resilience of financial institutions in the EU. TIBER-EU stands for Threat Intelligence-Based Ethical Red Teaming and comes from the European Central Bank (ECB). TLPT stands for Threat-Led Penetration Test under DORA. A TLPT follows a predefined attack scenario that is developed with a Threat Intelligence Provider based on current threats. It replicates the tactics, techniques, and procedures of real attackers. For more information, see our blog post “Enhancing Cyber Resilience Through Attack Simulations According to DORA and TIBER”.
DORA obliges companies in the financial sector to carry out digital operational resilience testing. It is aimed mainly at financial service providers in the EU, but also at IT service providers that serve such institutions as clients. TIBER mainly concerns the financial sector and the insurance industry. Tests under TIBER are not mandatory. For more information, see our blog post “Enhancing Cyber Resilience Through Attack Simulations According to DORA and TIBER”.
DORA requires two types of tests: testing of ICT tools and systems, and advanced testing based on threat-led penetration testing (TLPT). The first type of test applies to the entire financial sector except microenterprises. This type of test is due at least once a year. It covers all ICT systems and applications that support critical or important functions. Only systemically important financial entities with a high level of ICT maturity must carry out TLPT, at least every 3 years. The requirements are set out in Articles 24 to 27 of Regulation (EU) 2022/2554. For more information, see our blog post “Security Testing in Accordance with DORA (Digital Operational Resilience Act)”.
Oneconsult offers three services for TIBER projects and DORA TLPT: Targeted Threat Intelligence, red teaming, and TIBER-based readiness tests. As a Threat Intelligence Provider, Oneconsult creates a threat analysis that is tailored to your company. Based on the scenarios from the Targeted Threat Intelligence report, the red team carries out multi-stage attack simulations. The readiness tests are for companies without a legal obligation and prepare them for such tests. Oneconsult has carried out complex red teaming projects in various countries, including projects under TIBER and projects based on TIBER. For more information, see our blog post “Enhancing Cyber Resilience Through Attack Simulations According to DORA and TIBER”.
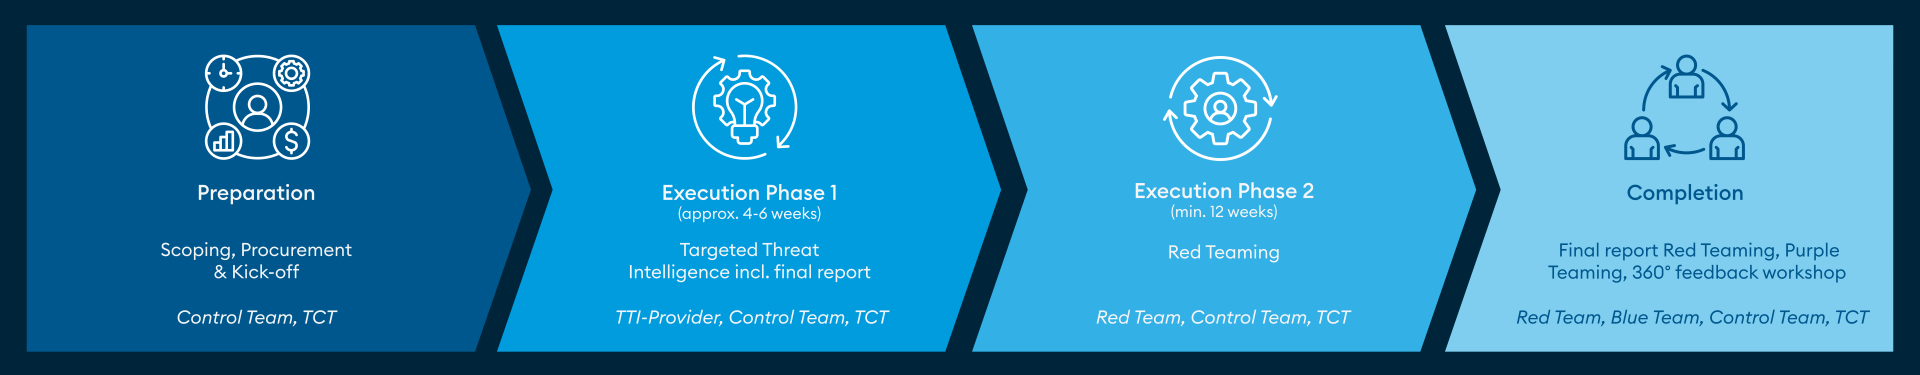
According to the BaFin procedure, a TLPT has three phases: preparation, testing, and closure. In the preparation phase, an attack scenario is developed from company-specific threat intelligence. In the testing phase, the testers attack according to this scenario. The blue team does not know the scenario. The TLPT Cyber Team of the supervisory authority oversees the test and confirms that it was carried out in compliance with the rules. In the closure phase, the results are analyzed, measures are defined, and the complete report is submitted to the supervisory authority. For more information, see our blog post “Security Testing in Accordance with DORA (Digital Operational Resilience Act)”.
A TLPT under TIBER or DORA usually takes several months. At its core, it includes a threat intelligence phase of around four weeks and a red teaming phase of at least twelve weeks. Scoping, documentation, purple teaming, and feedback rounds add to this. A complete TIBER-EU project often requires well over 200 person-days. For more information, see our blog post “Enhancing Cyber Resilience Through Attack Simulations According to DORA and TIBER”.
Classic red teaming is more flexible in scope than TIBER-EU and DORA TLPT. These are regulatory frameworks for threat intelligence-based red teaming in the financial sector, with fixed roles, phases, and mandatory purple teaming. A TIBER-EU project tests attack scenarios in full and continues even if the target institution detects individual attacks. It often requires well over 200 person-days. Oneconsult offers both forms. For more information, see our blog post “Enhancing Cyber Resilience Through Attack Simulations According to DORA and TIBER”.
A TIBER-based readiness test prepares companies for a possible future TIBER- or DORA-compliant test. It is suitable for companies that do not yet know whether they will be required to undergo such a test. The test reveals vulnerabilities and possible attack paths for cybercriminals. With the recommended measures from Oneconsult, you prepare your company for real threat scenarios in a targeted way.
Available Monday to Friday, 8:00 a.m. to 6:00 p.m. Exception: customers with an SLA should call the 24/7 IRR emergency number.
If you are a private individual, please contact your trusted IT service provider or your local police station.
You can find more information about our DFIR services here:
Don’t miss anything! Subscribe to our free newsletter.
